
"I’m very proud that InovaPrime has achieved ISO/IEC 27001:2022 certification and successfully completed our SOC® 2 Type II report. These significant milestones reflect our continued commitment to security and trust."
Marco Batista, InovaPrime’ CEO
Interview | October 13, 2026
Marco Batista, CEO of InovaPrime, shared the company’s key milestones and how InovaPrime continues to strengthen trust, security, and operational excellence.
Recently, InovaPrime achieved ISO/IEC 27001:2022 certification and successfully completed its SOC 2 Type II report What motivated the company to invest in these processes, and what were the main objectives behind these initiatives?
The decision to pursue ISO/IEC 27001:2022 certification and a SOC 2 Type II report was driven by InovaPrime’s commitment to trust, security, operational excellence and sustainable growth. As a provider of consulting services, managed services and the Governance.Business platform, we recognize that customers increasingly expect independent assurance that their information is protected and managed according to robust security and governance practices.
These initiatives were an important step in strengthening customer trust through independent assessment, demonstrating the strength of our security, risk management and operational practices, and supporting the growth of Governance.Business in increasingly demanding enterprise environments.
From a strategic perspective, they also help us align with the expectations of international customers and partners, while creating a strong foundation for future security, compliance and governance initiatives.
Obtaining ISO/IEC 27001:2022 certification and a SOC 2 Type II report require a rigorous assessment of internal controls, processes and security practices. How did these processes unfold within InovaPrime, and what were the main challenges encountered along the way?
While ISO/IEC 27001:2022 and SOC 2 Type II have different requirements and assessment approaches, they cover many complementary areas related to information security, processes, governance and risk management. For InovaPrime, working towards both frameworks at the same time created important synergies, allowing us to align efforts, strengthen common controls and make the overall process more efficient.
The process involved reviewing and strengthening policies, procedures, governance structures, operational practices, security controls, monitoring capabilities and evidence collection processes across the organization. In the case of SOC 2 Type II, this also meant demonstrating that controls operated effectively throughout the defined observation period. For ISO/IEC 27001:2022, the focus extended to establishing and maintaining an effective Information Security Management System, supported by a structured approach to risk management and continual improvement. This distinction reflects the respective nature of the two frameworks.
One of the main challenges was ensuring consistency and discipline throughout the process. It required strong collaboration between management, technology, operations, customer facing teams and platform stakeholders. Another challenge was transforming security and compliance activities into repeatable, measurable and continuously monitored processes rather than isolated initiatives.
Ultimately, working towards both frameworks reinforced a culture in which security, risk management, continual improvement and accountability are embedded into our daily operations rather than treated as separate compliance activities.
How do these achievements strengthen InovaPrime’s strategy and support its vision for sustainable and secure growth?
These achievements directly support InovaPrime’s vision of delivering innovative business solutions while maintaining strong standards of governance, security and operational reliability. The company has built its reputation around helping organizations improve strategy execution, governance, processes and service management. Achieving ISO/IEC 27001:2022 certification and obtaining a SOC 2 Type II report demonstrate that these same principles are applied internally.
From a strategic perspective, both frameworks strengthen our international positioning and enhance our differentiation in the market. They also support enterprise customer acquisition by helping address requirements during procurement and vendor assessment processes, while reinforcing long term credibility with customers and partners. Ultimately, they provide a stronger foundation for secure, scalable and sustainable international growth.
Trust and information security are now key factors when organizations select technology partners. How do you believe these internationally recognized frameworks enhance InovaPrime’s credibility among customers and partners?
Trust has become a critical purchasing criterion. Organizations want assurance that their technology partners manage information responsibly and maintain robust security controls.
ISO/IEC 27001:2022 certification and the SOC 2 Type II report provide independent assurance around InovaPrime’s approach to information security and relevant controls. Together, they give customers greater confidence that our security practices are not based solely on internal claims, but are independently assessed against recognized requirements and criteria.
For partners, these achievements demonstrate InovaPrime’s commitment to structured information security, governance and risk management practices. They can facilitate stronger collaboration, support vendor assessment processes and provide greater confidence when establishing long term business relationships.
As a company operating in both domestic and international markets, what impact do both frameworks have on InovaPrime’s commercial approach and business development efforts across different geographies?
The impact is particularly relevant in international markets and highly regulated sectors, where security and compliance requirements are becoming increasingly important elements of procurement processes.
In practical terms, these achievements can help streamline vendor due diligence, address security related requirements more effectively during sales cycles and strengthen our competitiveness in enterprise opportunities. They also provide recognized assurance that can support InovaPrime’s expansion into new geographies and facilitate stronger engagement with multinational organizations.
For many prospects, having this independent assurance can also help simplify supplier assessment activities by providing recognized evidence of our approach to information security and risk management.
Business plays a central role in InovaPrime’s portfolio. What is the significance of these achievements for the platform, and what additional assurance do they provide to the organizations that rely on it?
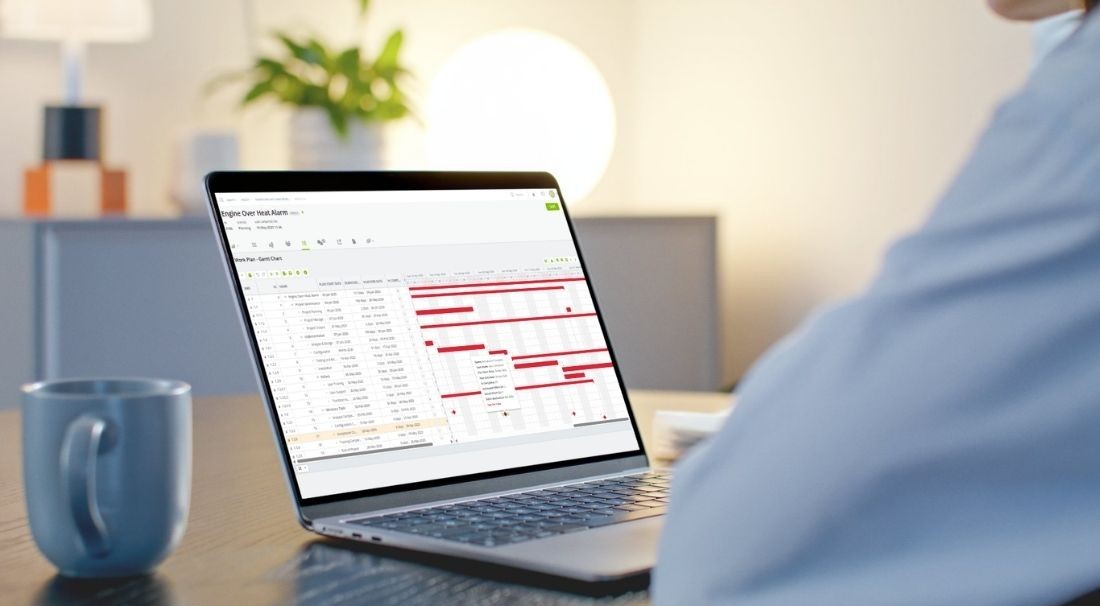
Governance.Business is a core platform designed to help organizations manage strategy, operations, governance, processes, portfolios, services and business performance through a consolidated solution.
ISO/IEC 27001:2022 certification and the SOC 2 Type II report provide customers with additional assurance that Governance.Business is supported by structured information security, operational and governance practices. Together, both frameworks provide independent validation of the relevant processes and controls that support the platform, within their respective scopes.
For customers, this translates into greater confidence in how information security and operational risks are managed. Relevant security controls and processes are subject to formal oversight and assessment, while information security is managed through a structured approach designed to evolve over time. Ultimately, these achievements reinforce the trust organizations can place in Governance.Business as a platform supporting critical management and governance activities.
In practical terms, what changes for InovaPrime customers following the ISO/IEC 27001:2022 certification and completion of the SOC 2 Type II report? What tangible benefits can they expect in terms of security, trust and risk management?
For customers, the most significant change is not in the functionality of our services, but in the level of assurance and transparency we can provide around how security and risk are managed.
ISO/IEC 27001:2022 certification and the SOC 2 Type II report provide independent evidence that relevant InovaPrime security and operational practices have been subject to rigorous external assessment. This can support customers in their own supplier assessments and provide useful evidence to their stakeholders, auditors and other relevant parties that they are working with a provider committed to recognized security, risk management and governance practices.
For us, that is one of the most tangible benefits of these achievements: strengthening trust through greater transparency and independent assurance.
With increasing regulatory requirements and growing concerns around cybersecurity, including initiatives such as NIS2 and DORA, how do ISO/IEC 27001:2022 and SOC 2 Type II complement this landscape and help customers address their own compliance and governance challenges?
NIS2, DORA and similar regulatory initiatives continue to raise expectations around cybersecurity, operational resilience, governance and third party risk management. NIS2 establishes cybersecurity risk management and reporting obligations for entities within its scope, while DORA establishes requirements around digital operational resilience within the financial sector, including ICT risk and third party risk.
While ISO/IEC 27001:2022 and SOC 2 Type II are not substitutes for compliance with specific regulatory requirements, they complement this evolving landscape by providing independent assurance around information security management and relevant controls. There are areas of common focus, but the scope and requirements of each remain distinct.
For customers, the assurance provided by ISO/IEC 27001:2022 certification and the SOC 2 Type II report can therefore form part of their broader governance, supplier risk management and compliance programs. It provides independently assessed evidence that can support their evaluation of InovaPrime as a technology partner.
Ultimately, this gives customers greater confidence that their technology ecosystem includes partners with a structured and independently assessed approach to information security, risk management and operational resilience.
Do you see these achievements as a final destination, or rather as another step in InovaPrime’s ongoing journey toward greater maturity in security, compliance and operational excellence?
These achievements are clearly another milestone rather than a final destination.
Security, compliance, and governance are continuous improvement disciplines. Threats evolve, customer expectations change, and regulatory requirements become more demanding. Maintaining a strong security posture therefore requires ongoing attention, investment, and adaptation.
Achieving ISO/IEC 27001:2022 certification and successfully completing the SOC 2 Type II audit recognizes the progress we have made so far, but they also reinforce our responsibility to continuously improve our processes, controls, monitoring capabilities and organizational resilience. This focus on continual improvement is also central to ISO/IEC 27001’s approach to information security management.
Ultimately, our view is that trust is earned every day. Continuous improvement is therefore not simply a compliance objective, but a strategic priority for InovaPrime.
What are the next steps InovaPrime is considering in terms of certifications, audits or other initiatives aimed at further strengthening customer trust and enhancing the company’s competitiveness?
Looking ahead, InovaPrime intends to continue investing in security, governance, operational excellence and customer trust.
Trust requires continuous effort. Our focus will remain on enhancing security controls and monitoring capabilities, strengthening our alignment with evolving regulatory requirements, and further developing our governance and risk management practices. Security will remain a strategic pillar for InovaPrime, supported by the ongoing evaluation of additional certifications and assurance initiatives in line with customer expectations and market demand.
At the same time, we will continue investing in Governance.Business to strengthen its governance, automation, security and resilience capabilities.
More broadly, our objective is not simply to achieve certifications or complete audits. It is to build a culture of excellence that supports sustainable growth, customer success and long term business value creation.